
Nginx代理+ CDN
我们使用运行nginx代理的VM (缓存关闭了)将主机重定向到正确的CDN url。
我们遇到的问题是,代理显示的旧内容与CDN上显示的内容不匹配。我们使用的CDN提供商是Verizon (通过由Verizon提供)。
当我们对原点进行更新时,我们会自动向CDN发送清除请求。这些可以是手动的和自动的动态更新,同时也可以是单个url清除和wilcard更新。似乎正在发生的事情是,当我们得到2个pruge请求接近的时候。第一个通过代理,而第二个没有。尽管两者在直接访问CDN url时都显示正确。
值得一提的是,这个问题发生的时间只有大约30%的。
nginx samle conf:
server {
    resolver 8.8.8.8;
    server_name <CUSTOM HOST>;
    location / {
      # Turn off all caching
      proxy_no_cache 1;
      proxy_cache_bypass 1;
      proxy_redirect off;
      expires -1;
      proxy_cache off;


      # Proxy settings
      proxy_set_header X-Forwarded-Host $http_host;
      proxy_set_header X-Real-IP       $remote_addr;
      proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
      proxy_headers_hash_max_size 512;
      proxy_headers_hash_bucket_size 128;

      # Override cache headers to set 2min browser cache
      proxy_hide_header Cache-Control;
      add_header Cache-Control max-age=120;

      proxy_pass "<CDN URL>request_uri";
    }
}
nginx.conf:
user www-data;
worker_processes auto;
pid /run/nginx.pid;
include /etc/nginx/modules-enabled/*.conf;

events {
    worker_connections 768;
    # multi_accept on;
}

http {

    sendfile off;
    tcp_nopush on;
    tcp_nodelay on;
    keepalive_timeout 65;
    types_hash_max_size 2048;


    include /etc/nginx/mime.types;
    default_type application/octet-stream;

    ##
    # SSL Settings
    ##

    ssl_protocols TLSv1.2 TLSv1.3;
    ssl_prefer_server_ciphers on;

    access_log /var/log/nginx/access.log;
    error_log /var/log/nginx/error.log;

    gzip on;

    include /etc/nginx/conf.d/*.conf;
    include /etc/nginx/sites-enabled/*;
}
下面是一个例子,CDN显示更新的内容,然后显示代理,我们有一个最后修改的不匹配:
CDN:
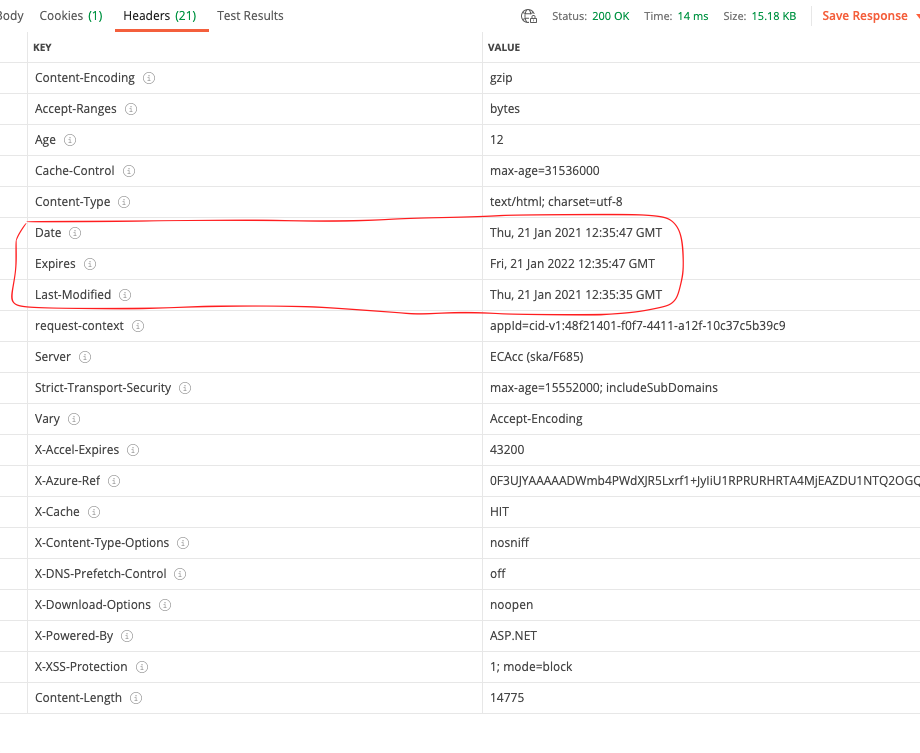
代理:
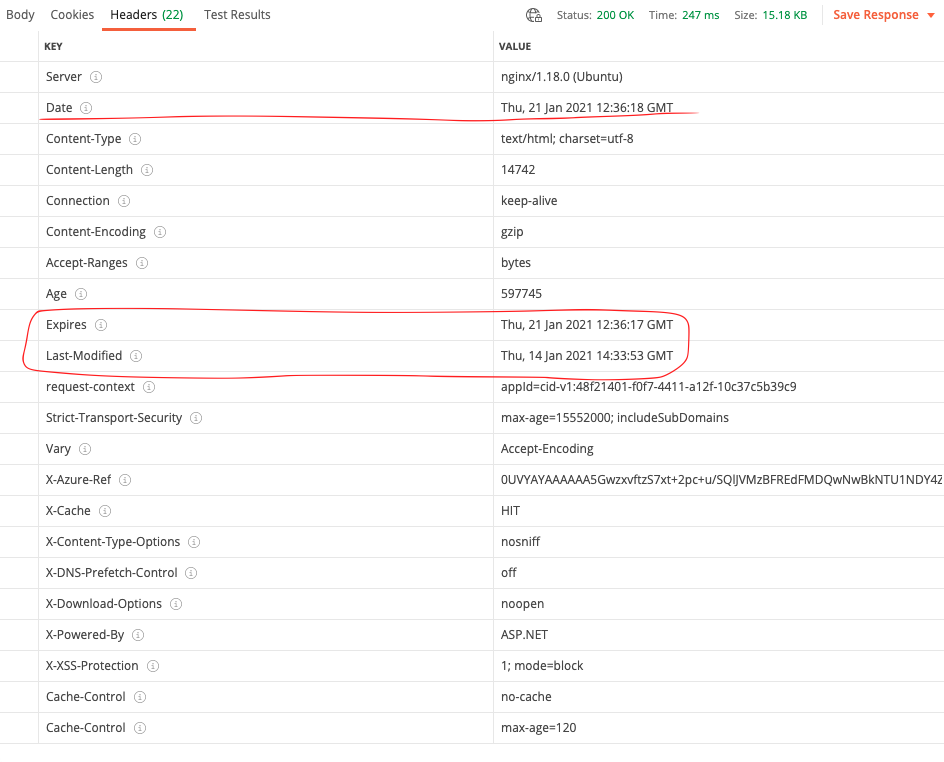
我尝试通过VPN查看代理是否遇到了特定的POP,但是所有的POP:s都显示了正确的内容。
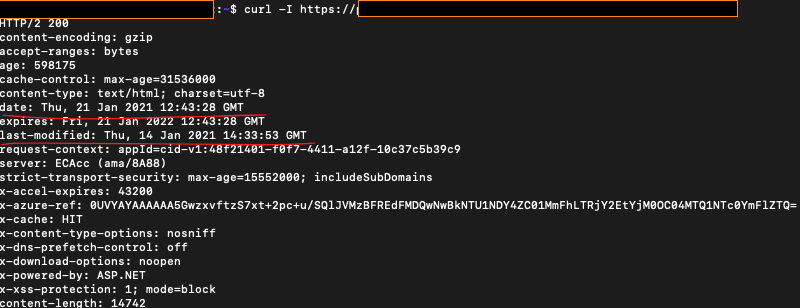
当出现错误时,从代理向CDN发送curl请求将导致相同的不正确的标头。
在我们执行清除之后,有几个请求直接传递到原点,直到CDN再次开始提供缓存的版本。
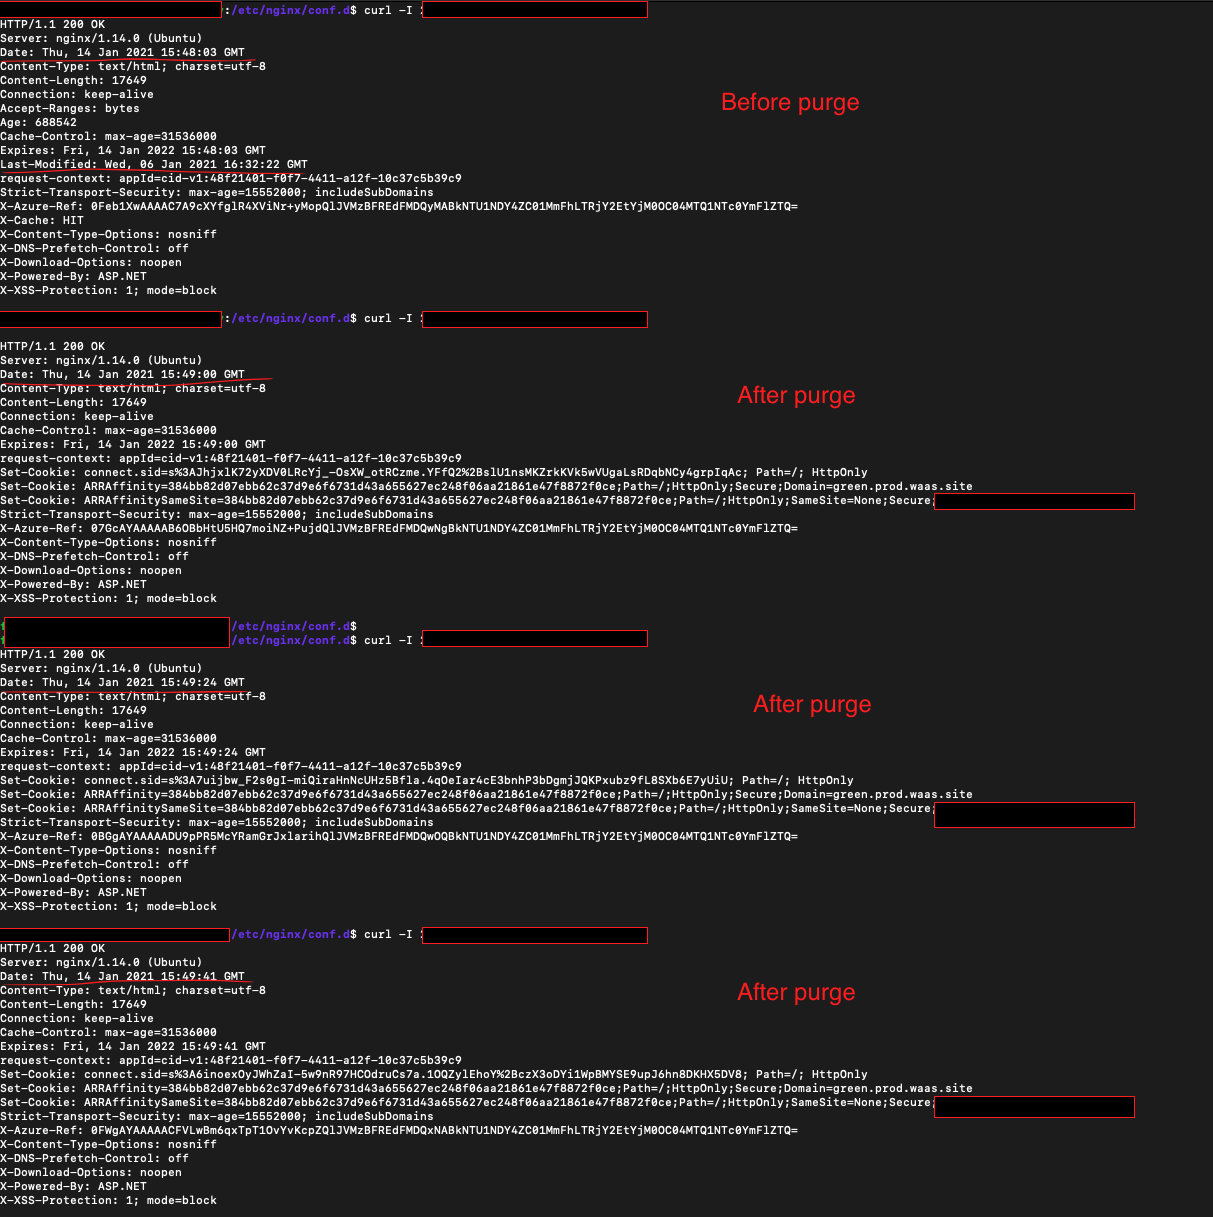
我们在大约1分钟后收到第一次命中。
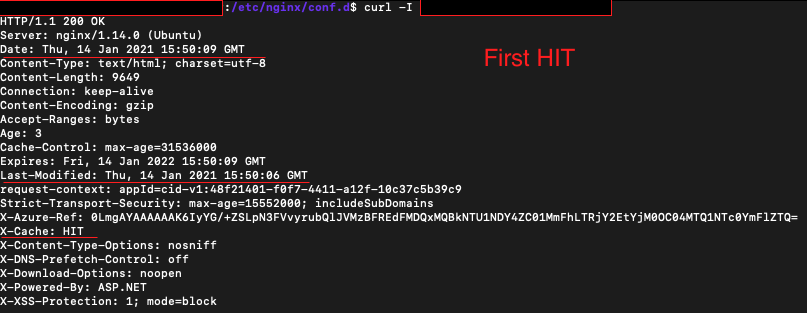
我开始认为这在内部可能与Azure & Verizon有关。所以我创建了一个在amazon上托管的完全复制的代理,但是错误似乎是预先出现的。在nginx中还有什么东西可以导致这种行为吗?
回答 1
Stack Overflow用户
发布于 2021-01-28 11:57:48
尝试添加,以查看页面是否被检索,每次命中。
add_header Last-Modified $date_gmt;
add_header Cache-Control 'no-store, no-cache, must-revalidate, proxy-revalidate, max-age=0';
if_modified_since off;
expires off;
etag off;https://stackoverflow.com/questions/65935043
复制相似问题
腾讯云开发者

Copyright © 2013 - 2026 Tencent Cloud. All Rights Reserved. 腾讯云 版权所有
深圳市腾讯计算机系统有限公司 ICP备案/许可证号:粤B2-20090059  粤公网安备44030502008569号
腾讯云计算(北京)有限责任公司 京ICP证150476号 | 京ICP备11018762号